
We are streamlining the Droplet ecosystem! Starting today, the official Droplet blog has a brand-new home at https://marketplace.droplet.is/blog.
By bringing our news, technical deep-dives, and server guides directly into the Droplet Marketplace, you now have a single unified hub for our products, tools, and engineering updates. Going forward, all new articles, security advisories, and platform announcements will be published exclusively on the Marketplace blog.
First Up on the New Blog: The “php2shell” Emergency Patch Guide
To kick things off on the new platform, we have just published an urgent security walkthrough covering CVE-2026-109618 and CVE-2026-109619—the critical 9.2 CVSS “php2shell” vulnerability affecting PHP web servers worldwide.
If you are running Drupal, Open Social, Drupal Commerce, WordPress, Laravel, or Magento on an Ubuntu DigitalOcean Droplet, your CMS dashboard may be misreporting your patch status—and simply relying on unattended-upgrades won’t clear vulnerable worker processes from memory without a service restart.
Our full breakdown covers:
- Why standard Ubuntu version numbers (like
8.3.6) can hide whether your server is actually patched. - The exact terminal commands to upgrade PHP and flush vulnerable
php-fpmworkers in under two minutes. - How to verify the
CVE-2026-109618andCVE-2026-109619patch entries directly inside your Debian changelog.
⚠️ Urgent Action Required for Server Admins:
Lock down your DigitalOcean Droplet in under two minutes by following our step-by-step guide here:
https://marketplace.droplet.is/blog/digitalocean/php2shell-emergency
Read the php2shell Patch Guide →
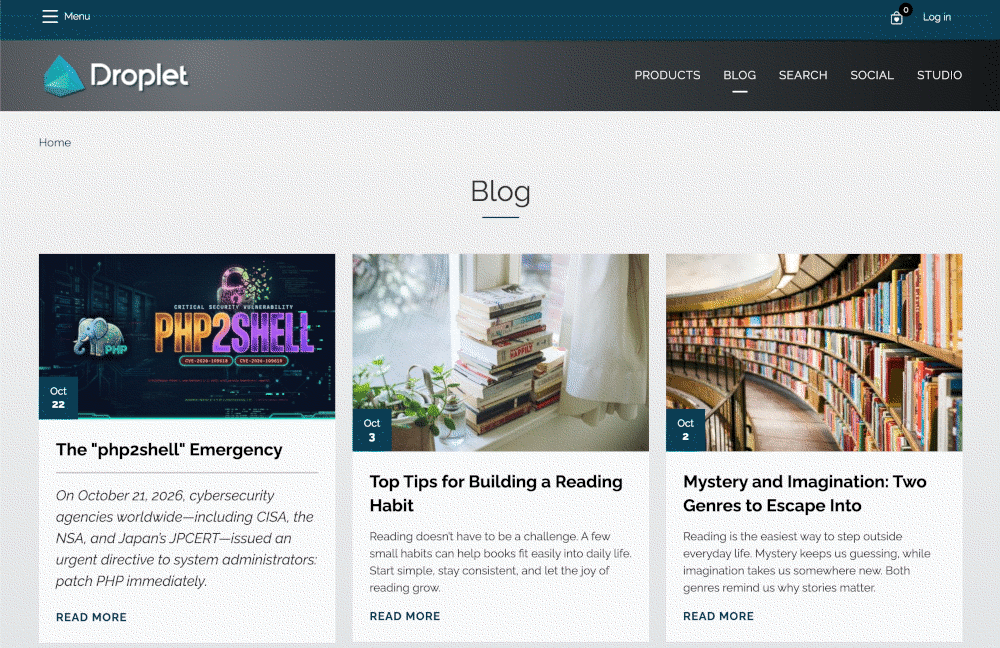
Update Your Bookmarks
Be sure to bookmark https://marketplace.droplet.is/blog so you don’t miss upcoming releases, infrastructure guides, and security alerts. See you over on the Marketplace!